Pakistan warns of AI-driven cyberattacks on banks, critical infrastructure
National CERT warns of AI-driven cyberattacks on Pakistan's banks and critical infrastructure, urging institutions to strengthen their digital defenses.
Business Desk
The Business Desk tracks economic trends, market movements, and business developments, offering analysis of both local and global financial news.
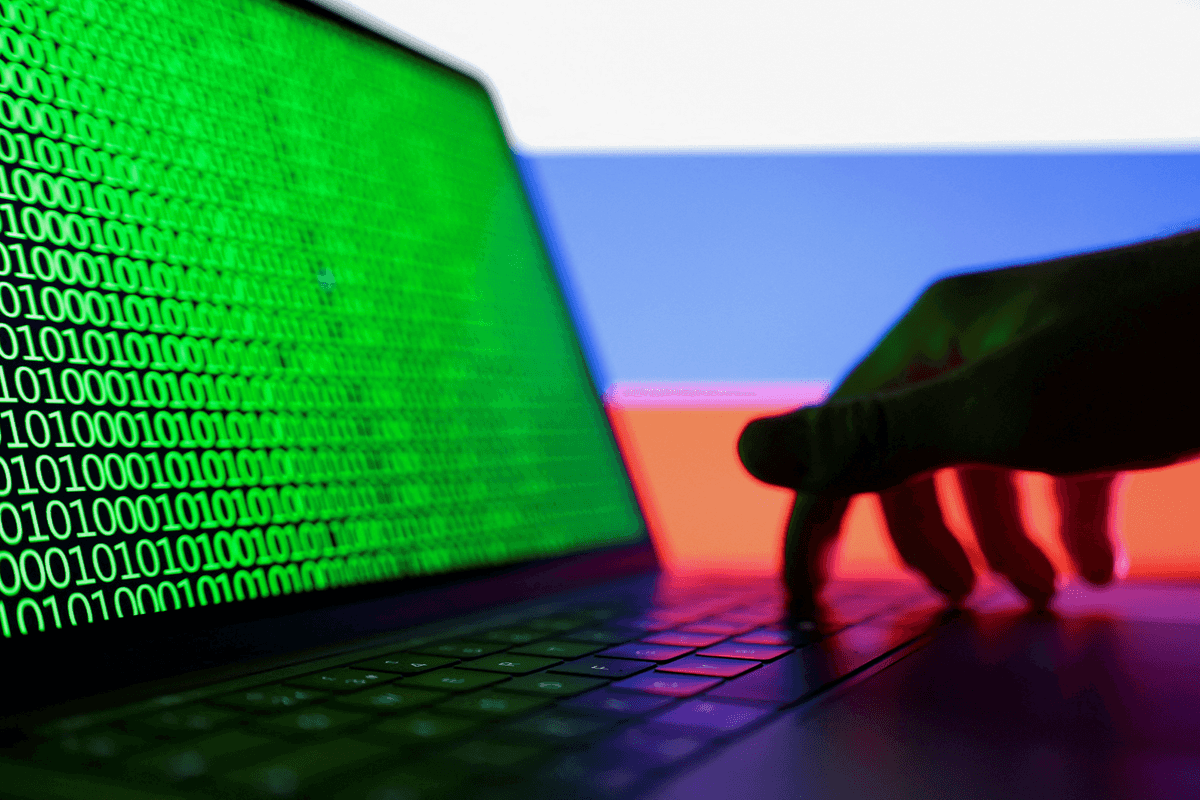
The advisory says hackers are increasingly using artificial intelligence, automated bots and advanced technologies to carry out cyberattacks.
File
Pakistan's National Cyber Emergency Response Team (National CERT) has issued an advisory warning of rising AI-driven cyberattacks on banks, financial institutions and critical infrastructure. The advisory urges all organizations to strengthen their cybersecurity measures against automated threats.
What is the National CERT advisory on AI-driven cyberattacks?
The advisory says hackers are increasingly using artificial intelligence, automated bots and advanced technologies to carry out cyberattacks. It names banks, payment platforms and essential services as likely targets, and directs institutions to protect their systems, data and infrastructure.
According to the advisory, hackers could target banks' online systems, digital banking services, payment platforms and customer data. Attackers may also display fake account balances to create fear and confusion among customers.
The advisory also warns of password theft and automated attacks using artificial intelligence. These methods could make it easier for hackers to target financial systems.
Which sectors face the biggest cyber threats in Pakistan?
Beyond banking, oil and gas facilities, and electricity generation and transmission systems are also exposed to cyber threats. Industrial control systems, water supply networks, transportation and other essential services could face disruptions.
National CERT has also identified third-party service providers and insecure remote access systems as potential vulnerabilities. Attackers could exploit both to gain entry into institutional networks.
What has National CERT asked institutions to do?
The response team has directed all institutions to strengthen their cybersecurity arrangements and take additional measures to protect their digital systems, sensitive information and critical infrastructure.
Comments
See what people are discussing