News Desk
The News Desk provides timely and factual coverage of national and international events, with an emphasis on accuracy and clarity.
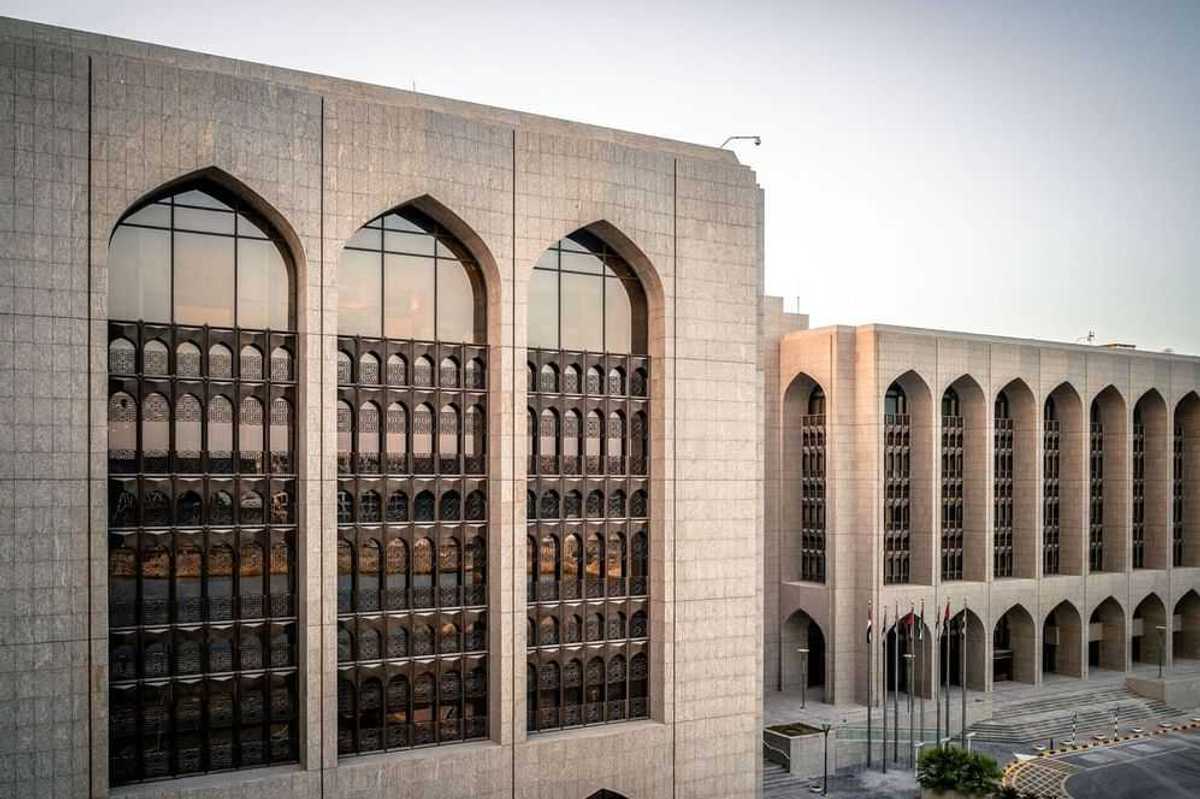
The Central Bank of the UAE's new Operational Risk Management Regulation took effect on September 14, 2026, requiring banks to report major incidents within four hours.
WAM
The Central Bank of the UAE introduced a new Operational Risk Management Regulation for all licensed financial institutions, Gulf News reported. The rule, known as Regulation No. C 1/2026, replaces the previous 2018 framework. It requires banks to report major disruptions within four hours and strengthens cybersecurity, testing and penalties across the sector.
What is the UAE Central Bank's new operational risk regulation?
The regulation sets minimum standards for how financial institutions manage operational risk and stay resilient during disruptions. It applies to all licensed institutions with legal personality, not just banks. The rule replaces Circular No. 163/2018 and adds new requirements covering cybersecurity, third-party risk, stress testing and incident reporting.
How does the three lines of defense structure work?
The regulation reinforces a three-tier risk structure within institutions. Business units form the first line and are responsible for spotting and controlling risks as they arise. Risk management and compliance teams make up the second line, providing independent oversight of business decisions.
Internal audit serves as the third line, offering independent assurance that the overall risk framework is working. Institutions must also maintain an independent operational risk function led by a Chief Risk Officer. This function assesses risks, reviews internal controls and trains staff on risk awareness.
Why does cybersecurity sit at the center of the new rules?
The regulation places cybersecurity and information technology risk at the core of operational risk management. Institutions must build frameworks covering risk identification, incident response, patch management, data governance and disaster recovery. These frameworks require regular updates to keep pace with new and emerging threats.
What testing will banks be required to carry out?
Financial institutions must run periodic stress tests and penetration tests on their systems. For critical functions, an independent external party must carry out the penetration testing, with results presented directly to the board of directors.
Institutions must also test their business continuity and disaster recovery plans under severe but realistic scenarios. Simply keeping a plan on file is no longer enough under the new framework.
How soon must banks report an incident to the Central Bank?
Institutions must alert the Central Bank within four hours of any event that significantly affects, or is likely to affect, critical operations. A brief follow-up report is due within 24 hours, covering the nature of the event, steps taken and expected recovery time.
The Central Bank must also be notified once normal operations resume. Separately, institutions must report any high-severity incident within 72 hours, based on their own incident classification criteria.
How are customers and fraud covered under the regulation?
The regulation requires institutions to clearly inform customers if operational errors lead to inaccurate account or transaction information. Institutions are held responsible for customer losses caused by their own errors, under existing consumer protection rules.
Both internal and external fraud now fall under the operational risk framework. Institutions must identify, monitor and report fraud incidents as part of their broader risk management process.
What penalties can banks face for non-compliance?
Violations of the regulation can bring administrative or financial penalties. The Central Bank can remove or restrict senior management and board members, arrange temporary management of an institution, impose fines or bar individuals from working in the UAE financial sector.
What changes for financial institutions under the new rules?
New elements not present in the 2018 rules include operational resilience, mapping of interdependencies, third-party risk management, stress testing, four-hour incident reporting, data governance and public disclosure.
Institutions are expected to review governance structures, reassess critical operations and test continuity plans rather than simply document them. They must also strengthen cybersecurity and build stronger risk-reporting systems reaching the board and the Central Bank.

Comments
See what people are discussing